
Hello Habr! Have you ever wondered why your written parser, which thoroughly copies the browser headers, is suddenly completely blocked by the site’s security on the second request? It seems that the User-Agent is correct, and the proxies are high-quality, but the server still answers: You are a bot and also adds a captcha on top.
Every time a browser opens a page, an application accesses an API, or another parser collects data, almost always the same scenario occurs - a secure connection is established via TLS. We are used to taking it for granted: the browser has verified the certificate, agreed with the server on encryption, and then we can safely transfer data. But there is one caveat: encrypting the traffic content does not mean that the client remains invisible to the server.
Even before the application sends the first HTTP request, the client manages to tell a lot about itself. The set of supported ciphers, the order of TLS extensions, the parameters of cryptographic groups, and even the features of subsequent communication via HTTP/2 form a kind of digital signature. According to it, modern WAF and anti-fraud systems are able to distinguish a regular browser from a script, console curl, or a self-written client in Go.
In this article, we will understand how the TLS handshake works, how versions TLS 1.0 and 1.3 differ, and why even the transition to more modern cryptography did not save clients from network sniffing. Let's see how the JA3 and JA4 algorithms work, why a single TLS fingerprint is not enough, and what additional information can be obtained from HTTP/2. And then let's move on to practice: we'll figure out how to manage a TLS fingerprint using uTLS in Go and how to use Finch to analyze and filter incoming traffic.
Historical background: from Netscape's ambitions to the design of modern TLS ciphers
In the mid-90s, the Internet ceased to be a toy for academics and began to rapidly transform into a global marketplace. The main problem of the nascent e-commerce was absolute network transparency: credit card data and passwords flew over HTTP in clear text, accessible to any intermediate router. Realizing that without privacy, business would not take off, engineers at Netscape, led by Taher Elgamal, sat down to design a solution in 1994. Their first attempt, the SSL 1.0 protocol, contained so many cryptographic childhood diseases (like vulnerabilities to replay attacks) that they did not even dare to release it to the public. SSL 2.0, which debuted in 1995, made it to release in the Netscape Navigator 1.1 browser, but also turned out to be leaky like a sieve. It was only with version SSL 3.0 (1996) that the architecture was perfected. Later, the IETF consortium took SSL 3.0 as a basis, refined hash functions for key generation, and in 1999 introduced the world to the independent open standard TLS 1.0 (technologically it was SSL 3.1). Thus began the era of transportation security: it was this evolution that laid the foundation for the cryptographic handshake that today protects trillions of terabytes of global traffic.
How elliptic curves saved processors
In the era of early TLS, the classic asymmetric cryptography RSA was in charge - it was responsible for verifying the authenticity of the server and generating public keys. To protect the session, devices had to manipulate huge prime numbers. The problem emerged in the late 2000s with the advent of the smartphone era: the mobile Internet was growing, and the weak processors of the first gadgets literally melted from the need to calculate huge 2048-bit keys. At this moment, elliptic curve curves (ECC) came out. Their mathematics was that a curve like 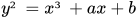 provided the same resistance, but with an extremely short key length. For example, the modest 256-bit key of the popular X25519 curve provided RSA-3072 level security. The transition to ECC in conjunction with ECDHE class algorithms not only reduced the load on servers and mobile chips, but also gave the Internet direct secrecy.
Because the Internet is made up of millions of completely different devices—from ancient ATMs to cutting-edge servers—TLS was designed to be flexible. To ensure that the client and server understand each other, engineers came up with cipher suites. These are long lines of instructions, collected as combo meals at KFC. For example, the TLS_ECDHE_RSA_WITH_AES_128_GCM_SHA256 cipher stated: the ECDHE elliptic curve protocol is responsible for secure negotiation of the primary secret, the authenticity of the server itself is still certified by the good old RSA, and the traffic is encrypted and checked for integrity using AES-GCM. And SHA256 works as a controller, it generates shared encryption keys and protects the connection process itself from outside interference.
Evolution of handshakes: from TLS 1.0 to TLS 1.3
To understand how modern anti-fraud systems calculate users based on the first network packet, you need to analyze the logic of interaction between the browser and the server at the L4 OSI transport layer. Each generation of protocols tried to solve two problems: make the connection secure and reduce latency.
In the TLS 1.0–1.2 era, the handshake process required two full roundtrips (2 RTT). The browser sent a Client Hello packet with a list of supported versions, cipher suites and extensions. The server selected a combination in Server Hello, attached its digital certificate and sent parameters for generating keys. Only after the second round of agreement was encryption turned on.


There were two problems with this scheme. The first is high delays due to unnecessary network requests. The second is excessive openness: the server certificate, browser extensions and compression methods were transmitted in their pure form. Any passive sniffer could study the session parameters before enabling crypto protection. In addition, the absence of Perfect Forward Secrecy made it possible in the future to decrypt historical traffic if the private key was compromised.
TLS 1.3 (2018) reduced the introduction procedure to one round (1 RTT) and removed dozens of legacy ciphers, leaving five strong options based on AEAD. Now the browser immediately sends key blanks for popular cryptographic groups to Client Hello, and the server accepts one of them in the response packet. When visiting again, the session ticket mechanism (0-RTT) allows you to send an encrypted HTTP request immediately in the first packet.
As an example, let's look at Client Hello when accessing GitHub via Wireshark:


In TLS 1.3, all server messages, including the site certificate, are encrypted immediately after receiving the key template from the client. Only the first Client Hello remains open to an external observer.
Since Cloudflare, WAF and anti-fraud platforms have lost the ability to analyze certificates and subsequent stages of a handshake, they have focused on the only visible detail. The structure, order of ciphers and extensions in the unencrypted Client Hello package have turned into a unique digital signature, which is used to identify bots today.
Digital Handwriting: The Anatomy of TLS Fingerprinting (JA3 and JA4)
Because TLS 1.3 hides all subsequent handshake steps behind cryptography, the Client Hello packet has become the primary identity token. The idea behind TLS fingerprinting is simple: each network stack—whether it’s the engine in Google Chrome, the curl library, the requests Python package, or a custom Go Trojan—generates this first message in its own way. The order of cipher suites, the composition of extensions, and supported elliptic curve formats are hardcoded in the client code. This is an ideal marker for defense systems. Why analyze the behavior of a bot if it can be cut off at distant approaches simply because its network stack declares itself like Chrome in HTTP headers, but says hello in TLS like an old Python script?
For a long time, the JA3 algorithm, developed by Salesforce engineers in 2017, remained the absolute standard in this area. The mechanics of JA3 are simple to the point of genius: strictly five parameters are extracted from the raw Client Hello package in a specific order - TLS version, list of supported cipher suites (Cipher Suites), list of extensions (Extensions), supported elliptic curves (Supported Groups) and elliptic curve formats (Elliptic Curve). Values within each category are written separated by commas, and the categories themselves are separated by a hyphen. The resulting text string is run through the MD5 hash function. This final 32-character hash is the JA3 fingerprint. If WAF sees a request to the authorization endpoint with a hash that is Googled as a standard fingerprint of the sqlmap utility, the session is instantly dropped.
[JA3 Fullstring: 771,4865-4866-4867-49195-49199-49196-49200-52393-52392-49171-49172-156-157-47-53,51764-16-65281-35-23-45-0-65037-13-5-11-43-51-27-10-17613-18-41,4588-29-23-24,0]
[JA3: 2a91540461ce04bac4c1c785ce9fa811]
However, over time, JA3 developed serious architectural problems that became critical for TLS 1.3. The first problem is fragility: since JA3 takes into account absolutely all extensions and ciphers in the order in which the client spat them out, any minimal change (for example, if the browser was updated and added one new extension to the end of the list) completely changes the MD5 hash. The second and main problem is Google's TLS Randomization Initiative (GREASE).

To prevent network equipment vendors from sharpening their parsers for specific bytes, modern browsers deliberately mix random garbage ciphers and extensions from a special range into Client Hello with each new handshake. For JA3, this was a disaster: the same legitimate Chrome, with five page reloads, generated five completely different MD5 fingerprints, which made classic blacklists ineffective against smart clients. If you open Wireshark and run traffic capture, you will see with your own eyes how JA3 fingerprints jump from session to session on the same device.
[JA3 Fullstring: 771,4865-4866-4867-49195-49199-49196-49200-52393-52392-49171-49172-156-157-47-53,51-13-10-65037-23-43-45-27-0-16-65281-35-5-11-51764-17613-18-41,4588-29-23-24,0]
[JA3: 7420fb81d80ea49cb26bf1b355881c06]
To finally understand the scale of the disaster, just look at real Client Hello fingerprints of the same browser, collected within a few seconds of each other. In the first session, the raw parameter string looks like 771,4865-4866-4867-49195-49199-49196-49200-52393-52392-49171-49172-156-157-47-53,51-13-10-65037-23-43-45-27-0-16-65281-35-5-11-51764-17613-18-41,4588-29-23-24,0, which after hashing gives a strict MD5 fingerprint 7420fb81d80ea49cb26bf1b355881c06. But as soon as the user simply refreshes the page, the same network stack generates another string: 771,4865-4866-4867-49195-49199-49196-49200-52393-52392-49171-49172-156-157-47-53,51764-16-65281-35-23-45-0-65037-13-5-11-43-51-27-10-17613-18-41,4588-29-23-24,0. With the ciphers and elliptic curves unchanged, the third group - the list of extensions - was completely shuffled, and the number 51764 came out on top. In hexadecimal, this is 0xCAAC, typical dynamic garbage from the GREASE reserved pool. Because of this minimal noise, the output is a completely new hash 2a91540461ce04bac4c1c785ce9fa811. For any classic WAF, these two requests look like visits from two completely unfamiliar and unrelated clients, which completely nullifies the effectiveness of the old signature databases.
New standard: JA4+
The aging standard was replaced by the JA4+ family of algorithms, announced in 2023. JA4 radically changes the logic of fingerprinting, making the fingerprint not just a blind hash, but an easily human-readable string that is resistant to GREASE randomization. The basic JA4 client fingerprint consists of three text blocks separated by underscores, each representing a different level of abstraction.
The first block, JA4_A, collects soft properties as a 10-character code. The first character indicates the transport type (t for TCP, q for QUIC, d for DTLS), the next two indicate the TLS version (for example, 13). Then there is one SNI presence character (d - domain specified, i - IP specified/absent). Next, the number of ciphers (2 digits), the number of extensions (2 digits) and two characters taken from the first and last character of the ALPN protocol are recorded (for example, h2 for HTTP/2 or 00 if there is no ALPN). It is important that all GREASE values are completely excluded from this block, due to which the overall structure of the package remains stable under any conditions.
The second block, JA4_B, is responsible for the hash of the ciphers. Here a list of all supported Cipher Suites is taken (again, with automatic cutting of random GREASE bytes), sorted in ascending numbers and hashed using the SHA-256 algorithm, from which the first 12 characters are included in the final fingerprint. Sorting is a solution to the problem when clients change the order of ciphers for the sake of optimization, completely breaking the old JA3. Finally, the third block, JA4_C, processes the list of extensions: they are also sorted in ascending order without taking into account GREASE (with the exception of SNI and ALPN), and then the signature algorithms are added to them in their original order. The resulting string is turned into a second 12-character SHA-256 hash.
[JA4: t13d1518h2_8daaf6152771_e2d80978ab2e]
[JA4_r: t13d1518h2_002f,0035,009c,009d,1301,1302,1303,c013,c014,c02b,c02c,c02f,c030,cca8,cca9_0005,000a,000b,000d,0012,0017,001b,0023,0029,002b,002d,0033,44cd,ca34,fe0d,ff01_0904,0905,0906,0403,0804,0401,0503,0805,0501,0806,0601]
Let's look at the actual print above and its raw format:
In block A (
t13d1518h2) we immediately read the connection context: the client runs on the TCP protocol (t), uses TLS 1.3 (13), specified a domain name in SNI (d), offers exactly15ciphers and18extensions (excluding GREASE), and also plans to communicate using the HTTP/2 protocol (h2).Block B (
8daaf6152771) hides the SHA-256 hash from the cipher list. By pre-sorting in ascending order, this hash will remain unchanged even if the client deliberately shuffles their order.In block C (
e2d80978ab2e) there is an encrypted list of TLS extensions, previously cleared of SNI and ALPN and sorted in ascending order, to which the signature algorithms (0904,0905...0601) are glued at the tail in their original, native order.
While JA3 can easily be bypassed by bot developers by simply shuffling extensions to change the resulting MD5 hash, the JA4 protocol allows security systems to be much more flexible. Even if an automated script tries to shuffle extensions or mix in random bytes, the JA4_A block and the pre-sorted B and C blocks will remain identical to the original browser. Moreover, analysis systems can now block clients selectively: for example, allow traffic if blocks B and C are valid for Chrome, but drop the session if block JA4_A shows that the client is trying to work using HTTP/1.1 where a real browser is required to use HTTP/2.
P.S if you are too lazy to download wireshark and configure it, then there is site to view your browser tls fingerprint.

There you can test your implementations of uTLS or scripts on different endpoints:

Anatomy of HTTP/2 fingerprinting
After a successful TLS handshake, communication between the client and server moves to the application layer. For modern websites, this almost always means switching to the HTTP/2 protocol. At this stage, security systems receive the second echelon of identification - h2 fingerprinting. It’s not enough for a bot to simply imitate the browser’s TLS greeting; it needs to reproduce the mechanics of its HTTP engine without errors. Unlike text HTTP/1.1, binary HTTP/2 protocol works through frames. Immediately after opening a session, the client must send configuration starter packages to the server. The order of these frames, limits and thread priorities depend on the specific networking library. Why would an attacker spend colossal resources on a perfect forgery of the JA4 TLS fingerprint if his script would give itself away on the very first HTTP/2 frame, sending settings that real Google Chrome has not used for several years?
For a long time, the standard for analysis remained the HTTP2-fingerprint algorithm developed by Akamai and Salesforce engineers, which collects a hash of four key parameters of a binary session:
Akamai HTTP/2 fingerprint
MD5-хеш
52d84b11737d980aef856699f885ca86
Фрейм SETTINGS
1:65536;2:0;4:6291456;6:262144|15663105|0|m,a,s,p
SETTINGS_Frames (
1:65536;2:0;4:6291456;6:262144): List ofkey:valuepairs from the starting settings frame. Here the client specifies its limits: for example, the maximum number of parallel threads or the initial size of the sending window. Each parameter has its own ID, the resulting string is formed asID:значение, separated by semicolons. In this example, the client declares the HPACK compression table size to be 65,536 bytes (1:65536), disables Server Push (2:0), sets the initial stream window to 6 MB (4:6291456), and sets the maximum header list size to 256 KB (6:262144).WINDOW_UPDATE_Frame (
15663105): The window value from the flow control frame that the client sends next to set the buffer size for the entire connection (about 15 MB in the example).PRIORITY_Frames (
0): Parameters for prioritizing traffic flows, where the IDs of dependent flows and their weights are indicated. If there is no frame or priority mechanisms are not explicitly enabled,0or an empty string is given.Pseudo-Header Order (
m,a,s,p): The order of HTTP/2 service pseudo-headers. Letterhead markers are written separated by commas. The sequencem,a,s,pis deciphered by the first letters::method,:authority,:scheme,:path. Chromium-based browsers always send them in this order, while Firefox or custom network libraries use other combinations.
The resulting string is hashed via MD5, forming a unique 32-character session fingerprint. If WAF captures a legitimate TLS fingerprint for a Windows browser, but the HTTP/2 hash associated with it matches the specific handwriting of the curl console utility or the Hyper library, the request is classified as an attempt to spoof and is blocked.
However, classic h2 fingerprinting is tied exclusively to session binary frames, parameters that browsers regularly optimize, which produces entities in signature databases. In response to this, the JA4H (JA4 HTTP) module was introduced for detailed analysis of the HTTP requests themselves.

Instead of frames, JA4H is decomposed into clear blocks and hashes the context: the request method, the protocol version, the exact number of text headers (not counting Cookie and Referer), their alphabetical order and the presence of specific markers.
The combination of TLS and HTTP/2 fingerprinting creates a powerful two-level filter for WAF: it is no longer enough for automated scripts to simply replace the User-Agent - they have to completely recreate the behavior of a real browser, from TLS 1.3 cryptography to the structure of binary frames. However, for modern security systems like Cloudflare, these technical fingerprints (including JA4) serve only as a basic foundation. Analyzing colossal volumes of global traffic, advanced filters enrich fingerprints with AI-powered behavioral analysis. They evaluate IP reputation, request speed and network latency in real time, so even a perfectly emulated fingerprint will be instantly blocked if its contextual behavior does not match the patterns of a live user.
Masking using uTLS
Why does the standard net/http give out a bot? Let's imagine a typical situation: we are writing a parser in Go, adding headers User-Agent, Accept, Accept-Language and other attributes typical for Google Chrome to the request. At first glance, the request looks quite convincing. However, after sending it through a standard net or http server, it can instantly determine that it is not a browser at all. The reason lies in the fact that HTTP headers and the TLS fingerprint are formed at different levels.
The User-Agent header is just a string that the client passes to the server at the L7 HTTP layer. It has no effect on which cipher suites, extensions, or cryptographic groups are sent in the Client Hello message. The Go standard library uses its own TLS implementation (crypto/tls), which forms the handshake according to its internal logic. This results in a critical discrepancy: at the HTTP level, the client pretends to be Chrome, but at the TLS level, it displays a distinctive Go fingerprint.
Managing the TLS handshake
The uTLS library is a fork and extension of the Go TLS implementation, based on crypto/tls but providing low-level control over the Client Hello message. Its key feature is the ability to use pre-prepared profiles of popular clients, including Chrome, Firefox and Safari. Instead of manually assembling each handshake parameter, the developer selects a ready-made preset that completely mimics the TLS hello structure of the desired browser. In practice, this means that we are completely replacing standard Go behavior with Chrome logic before the first TLS packet is sent. The library will generate a list of cipher suites and extensions in accordance with the selected preset.
The most critical mistake when working with TLS mimicry is to set up a preset once and forget about it. Browsers are constantly updated, and along with them, their TLS fingerprints are updated. Chromium developers regularly modify their cryptographic stack: introducing SNI (Encrypted Client Hello / ECH) encryption, making support for post-quantum algorithms mandatory (such as ML-KEM / X25519MLKEM768), abandoning outdated cipher suites or changing the logic of TLS padding.
Sending a request with a Chrome profile
Let's look at an example where we intercept the creation of a TLS connection and establish it ourselves using uTLS:
This code is for educational purposes only and is far from a good implementation.
package main

import (
	"context"
	"fmt"
	"io"
	"log"
	"net"
	"strings"
	"time"

	http "github.com/useflyent/fhttp"
	utls "github.com/refraction-networking/utls"
)

func main() {
	fmt.Println("=== Выберите эндпоинт для проверки отпечатка ===")
	fmt.Println("1 - All of the information (/api/all)")
	fmt.Println("2 - Only fingerprints      (/api/clean)")
	fmt.Println("3 - Only TLS data          (/api/tls)")
	fmt.Print("Введите цифру (1-3): ")

	var choice int
	_, err := fmt.Scanf("%d", &choice)
	if err != nil || choice < 1 || choice > 3 {
		log.Fatal("Некорректный ввод. Введите число от 1 до 3.")
	}

	var path string
	switch choice {
	case 1:
		path = "/api/all"
	case 2:
		path = "/api/clean"
	case 3:
		path = "/api/tls"
	}

	baseURL := "https://tls.peet.ws"
	fullURL := baseURL + path

	transport := &http.Transport{
		DialTLSContext: func(ctx context.Context, network, addr string) (net.Conn, error) {
			host, _, err := net.SplitHostPort(addr)
			if err != nil {
				return nil, err
			}

			rawConn, err := (&net.Dialer{
				Timeout: 10 * time.Second,
			}).DialContext(ctx, network, addr)
			if err != nil {
				return nil, err
			}

			config := &utls.Config{
				ServerName: host,
				// Указываем h2 для ALPN-согласования на уровне TLS
				NextProtos: []string{"h2", "http/1.1"},
			}

			// Используем профиль автоматического подбора отпечатка Chrome
			conn := utls.UClient(rawConn, config, utls.HelloChrome_Auto)

			if err := conn.HandshakeContext(ctx); err != nil {
				conn.Close()
				return nil, err
			}

			return conn, nil
		},
		TLSHandshakeTimeout:   5 * time.Second,
		MaxIdleConns:          100,
		IdleConnTimeout:       10 * time.Second,
		ExpectContinueTimeout: 1 * time.Second,
		ForceAttemptHTTP2:     true,
	}

	client := &http.Client{
		Transport: transport,
		Timeout:   25 * time.Second,
	}

	req, err := http.NewRequest(http.MethodGet, fullURL, nil)
	if err != nil {
		log.Fatalf("Ошибка при создании HTTP-запроса: %v", err)
	}

	req.Header = http.Header{
		"cache-control":             {"no-cache"},
		"upgrade-insecure-requests": {"1"},
		"user-agent":                {"Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/146.0.0.0 Safari/537.36"},
		"accept":                    {"text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7"},
		"accept-language":           {"ru-RU,ru;q=0.9,en-US;q=0.8,en;q=0.7"},
		"priority":                  {"u=0, i"},

		// Задаем порядок обычных заголовков
		http.HeaderOrderKey: {
			"cache-control",
			"upgrade-insecure-requests",
			"user-agent",
			"accept",
			"accept-language",
			"priority",
		},

		// Задаем порядок псевдо-заголовков
		http.PHeaderOrderKey: {
			":method",
			":path",
			":authority",
			":scheme",
		},
	}

	fmt.Printf("\nОтправка запроса на %s...\n", fullURL)
	resp, err := client.Do(req)
	if err != nil {
		log.Fatalf("Не удалось выполнить запрос: %v", err)
	}
	defer resp.Body.Close()

	body, err := io.ReadAll(resp.Body)
	if err != nil {
		log.Fatalf("Не удалось прочитать тело ответа: %v", err)
	}

	fmt.Println("\n=== СЕТЕВАЯ ДИАГНОСТИКА ===")
	fmt.Println("Статус ответа сервера:", resp.Status)
	fmt.Println("Согласованный протокол:", resp.Proto)

	if strings.Contains(resp.Header.Get("Content-Type"), "application/json") {
		fmt.Println("\nДанные отпечатка от сервера (JSON):")
		fmt.Println(string(body))
	} else {
		fmt.Println("\nТело ответа (не JSON):")
		fmt.Println(string(body))
	}
}
Unique TLS fingerprint of the script above
=== Выберите эндпоинт для проверки отпечатка ===
1 - All of the information (/api/all)
2 - Only fingerprints      (/api/clean)
3 - Only TLS data          (/api/tls)
Введите цифру (1-3):
Отправка запроса на https://tls.peet.ws/api/clean...

=== СЕТЕВАЯ ДИАГНОСТИКА ===
Статус ответа сервера: 200 OK
Согласованный протокол: HTTP/2

Данные отпечатка от сервера (JSON):
{
  "ja3": "771,4865-4866-4867-49195-49199-49196-49200-52393-52392-49171-49172-156-157-47-53,45-11-27-51764-13-51-65281-35-23-0-65037-10-16-18-17613-5-43-41,4588-29-23-24,0",
  "ja3_hash": "efa0c28162e6cccca786c71779268784",
  "ja4": "t13d1518h2_8daaf6152771_e2d80978ab2e",
  "ja4_r": "t13d1518h2_002f,0035,009c,009d,1301,1302,1303,c013,c014,c02b,c02c,c02f,c030,cca8,cca9_0005,000a,000b,000d,0012,0017,001b,0023,0029,002b,002d,0033,44cd,ca34,fe0d,ff01_0904,0905,0906,0403,0804,0401,0503,0805,0501,0806,0601",
  "akamai": "1:65536;2:0;4:6291456;6:262144|15663105|0|m,a,s,p",
  "akamai_hash": "52d84b11737d980aef856699f885ca86",
  "peetprint": "GREASE-772-771|2-1.1|GREASE-4588-29-23-24|GREASE-2308-2309-2310-1027-2052-1025-1283-2053-1281-2054-1537|1|2|GREASE-4865-4866-4867-49195-49199-49196-49200-52393-52392-49171-49172-156-157-47-53|0-10-11-13-16-17613-18-23-27-35-41-43-45-5-51-51764-65037-65281-GREASE-GREASE",
  "peetprint_hash": "5fa343c29062ede7d0e28fd46c1052a7",
  "http_version": "h2"
}
A basic TCP connection is opened first, and the uTLS library masquerades it as a Chrome browser fingerprint using the HelloChrome_Auto profile, securely performing a TLS handshake while maintaining certificate and SNI verification.
Control is then passed to a custom fhttp library, which replaces Go's standard HTTP transport. Thanks to the ForceAttemptHTTP2 flag, it automatically switches the connection to the HTTP/2 protocol and allows you to manually configure the exact order of regular headers and pseudo-headers (:method, :path, etc.)
As an example, I’ll also give a unique curl fingerprint for mac:
~ curl https://tls.peet.ws/api/clean
{
  "ja3": "771,4867-4866-4865-52393-52392-52394-49200-49196-49192-49188-49172-49162-159-107-57-65413-196-136-129-157-61-53-192-132-49199-49195-49191-49187-49171-49161-158-103-51-190-69-156-60-47-186-65-49169-49159-5-4-49170-49160-22-10-255,43-51-0-11-10-13-16,29-23-24-25,0",
  "ja3_hash": "375c6162a492dfbf2795909110ce8424",
  "ja4": "t13d497h2_0d8feac7bc37_7395dae3b2f3",
  "ja4_r": "t13d497h2_0004,0005,000a,0016,002f,0033,0035,0039,003c,003d,0041,0045,0067,006b,0081,0084,0088,009c,009d,009e,009f,00ba,00be,00c0,00c4,00ff,1301,1302,1303,c007,c008,c009,c00a,c011,c012,c013,c014,c023,c024,c027,c028,c02b,c02c,c02f,c030,cca8,cca9,ccaa,ff85_000a,000b,000d,002b,0033_0806,0601,0603,0805,0501,0503,0804,0401,0403,0201,0203",
  "akamai": "3:100;4:10485760;2:0|1048510465|0|m,s,a,p",
  "akamai_hash": "64a832f547be33249bf4d33e8a46c5dc",
  "peetprint": "772-771-770-769|2-1.1|29-23-24-25|2054-1537-1539-2053-1281-1283-2052-1025-1027-513-515|0||4867-4866-4865-52393-52392-52394-49200-49196-49192-49188-49172-49162-159-107-57-65413-196-136-129-157-61-53-192-132-49199-49195-49191-49187-49171-49161-158-103-51-190-69-156-60-47-186-65-49169-49159-5-4-49170-49160-22-10-255|0-10-11-13-16-43-51",
  "peetprint_hash": "0d6ceceb9e71ec096d2022ad0651e2f2",
  "http_version": "h2"
}
Own Client Hello
If ready-made presets are not enough, uTLS allows you to fully control the request structure through the utls.HelloCustom mode. You can manually generate a list of TLS extensions and pass it to the library. This is necessary for compatibility testing, network stack analysis, or emulation of rare client versions.
However, manually building Client Hello requires a deep understanding of the protocol. TLS extensions often depend on each other, and their parameters must strictly correspond to general cryptography settings. A random or incorrect combination of elements will lead to an invalid handshake or to anomalies that are easily detected by the server.
Finch: filtering traffic using TLS fingerprints
Up to this point, we have looked at fingerprinting primarily from the client side. But what if we don't just want to look at JA3/JA4 in Wireshark, but use them to filter incoming traffic? To do this, you can try Finch - an open-source reverse proxy in Go from developer 0x4D31, which analyzes TLS handshake and HTTP requests, calculates JA3, JA4, JA4H and HTTP/2 fingerprints, and then makes decisions based on specified rules. Essentially, this is a small specialized proxy with a network fingerprint filtering mechanism, and not a full-fledged replacement for large commercial WAFs.
Let's say we already have an application running on the 8080, and Finch needs to accept HTTPS connections on the 8443 and proxy requests to the application. You can run it in simplified mode with the following command:
finch serve --listen :8443 --rules my.rules.hcl --upstream http://localhost:8080To begin with, you can not block traffic at all, but see what fingerprints come to the server. To do this, Finch has a separate mode echo, which starts a test server and returns information about the client and calculated fingerprints instead of proxying requests:
finch echo --listen :8443After launch, you can look at /fp/ to get a short JSON structure with fingerprints, or look at /fp/detail to see the most detailed data, including TLS ClientHello parameters, HTTP/2 headers and frames. This mode is good for experiments: you can send requests from Chrome, curl or a custom script, and then compare how the server sees them.
But the fun begins when we move from observation to filtering. Finch supports HCL-formatted rules that allow flexible processing of requests based on JA3, JA4, HTTP fingerprints, Suricata signatures and IP addresses. For example, the following rule demonstrates a hard lock on a client with a known suspicious JA3 ZMap scanner:
rule "block-scanner-ja3" {
  action = "deny"

  when {
    condition = tls.ja3 == "3518c438fe56bd7dba3f6e28example"
  }
}
If the TLS fingerprint matches the value listed, Finch will apply the deny action and instantly reject the request.
You can go further and take into account several signs at once, combining them. For example, a rule can be triggered if at least one of the suspicious traffic parameters matches. To do this, use the when any block:
rule "suspicious-client" {
  action = "tarpit"

  when {
    any = [
      tls.ja4 == "q13d0312h3_55b375c5d22e_c183556c78e2",
      http.ja4h == "bad-ja4h"
    ]
  }
}
The tarpit action is intended to intentionally slow down suspicious clients, similar to tarpit HAProxy. The same JA4 can be encountered by many legitimate users, and the browser's TLS profile changes over time. Therefore, it is more correct to first collect statistics, study real values, and only then add address rules for confirmed suspicious clients.
Finch has, so to speak, a nuance: the project is in active development, and its current version 0.1.0 is directly designated by the authors as experimental and not ready for a full release. Therefore, it should be considered primarily as an interesting tool for research and study of TLS fingerprinting.
The future of the protocol: ECH and its imprint
ECH (Encrypted Client Hello) is an approved RFC 9849 standard that hides SNI and other sensitive extensions such as ALPN from outside observers. With regular TLS 1.3, the domain is transmitted openly so that the server understands which site needs to be displayed. ECH solves this problem: the real parameters are packaged into a ClientHelloInner structure and encrypted using hybrid HPKE encryption, and a standardized stub ClientHelloOuter is passed outside. Although the standard mechanically allows pre-configuration of keys in the client, in practice, to securely obtain the ECHConfig structure, an encrypted DNS (DoH/DoT/DoQ) is required - otherwise the request will leak at the DNS stage. I just recently published an article where ECH support was added to Nginx and how it can all be configured.
For intermediate network fingerprinting on transit nodes, this means that external observers can no longer collect valid TLS fingerprints like JA3 or JA4. First, they only see a standardized external plug. Secondly, even if the client does not use ECH, the standard obliges it to use the GREASE ECH mechanism (sending empty random ECH fields), due to which real ECH sessions are not visually distinguished from the general traffic flow and are protected from selective blocking.
However, ECH does not completely hide traffic analysis. Security systems like WAFs inside the infrastructure still see the already decrypted internal handshake parameters. External providers can still analyze IP addresses, packet sizes, timings, as well as the behavior of the HTTP/2 and HTTP/3 protocols with their burst TCP/UDP connections, which differ greatly between script bots and real browsers. As a result, modern bot detection systems are finally moving from simple static TLS hashes to complex behavioral analysis of the entire set of user actions.
💬 Discussion 0
BBCode & Emoji supportedParticipate in discussions, ask authors questions, and share benchmarks by joining the ProArena engineering community.